Intent is the signature.
See every AI interaction. Read the intention inside it. Neutralize the hostile ones at the endpoint, before they execute.
See what others miss.
Neutralize what others only report.
See all AI activity
Across users, devices, applications and models — on the operating system and in the browser.
Comprehend the intent
Understand what the AI is trying to do, not just what it does.
Neutralize the hostile ones
At the point of interaction, before execution — without disrupting the rest.
Your teams adopted AI. Your controls never saw the plane it runs on.
Prompts, tool calls, coding copilots, and autonomous agents — the AI your workforce adopted moves through a plane your security stack was never built to watch, let alone stop. The exposure is already inside your environment. You just can’t see it yet.
Your employees are using AI tools you can’t see. Salience Cyber fixes that. It captures every AI interaction on the endpoint and turns it into one clean audit trail — visibility and enforcement in the same product, without an LLM sitting in the critical path or another EDR integration to maintain.
The exposure is measured, not asserted
Adoption outran governance. These figures show how wide the gap got, and what has already come through it.
All eight figures, with sources →
Sources
- [1] IBM Security, Cost of a Data Breach Report 2026, July 2026. Source for every figure marked [1]. ibm.com/reports/data-breach
- [2] IBM Newsroom, “One in Four Malicious Breaches are AI-Enabled, Costing Companies $6 Million on Average,” 29 July 2026. Source for the ~$6M average across the whole class of AI-enabled malicious breaches. newsroom.ibm.com
What you are left with
- Salience CyberThe hostile interaction is neutralized before it executes
- Model-judged AI securityA verdict from a model, and an alert
- Post-collection analyticsA report
- The stack you already ownA ticket
- Policy onlyAn assumption that people complied
This is what seeing it looks like
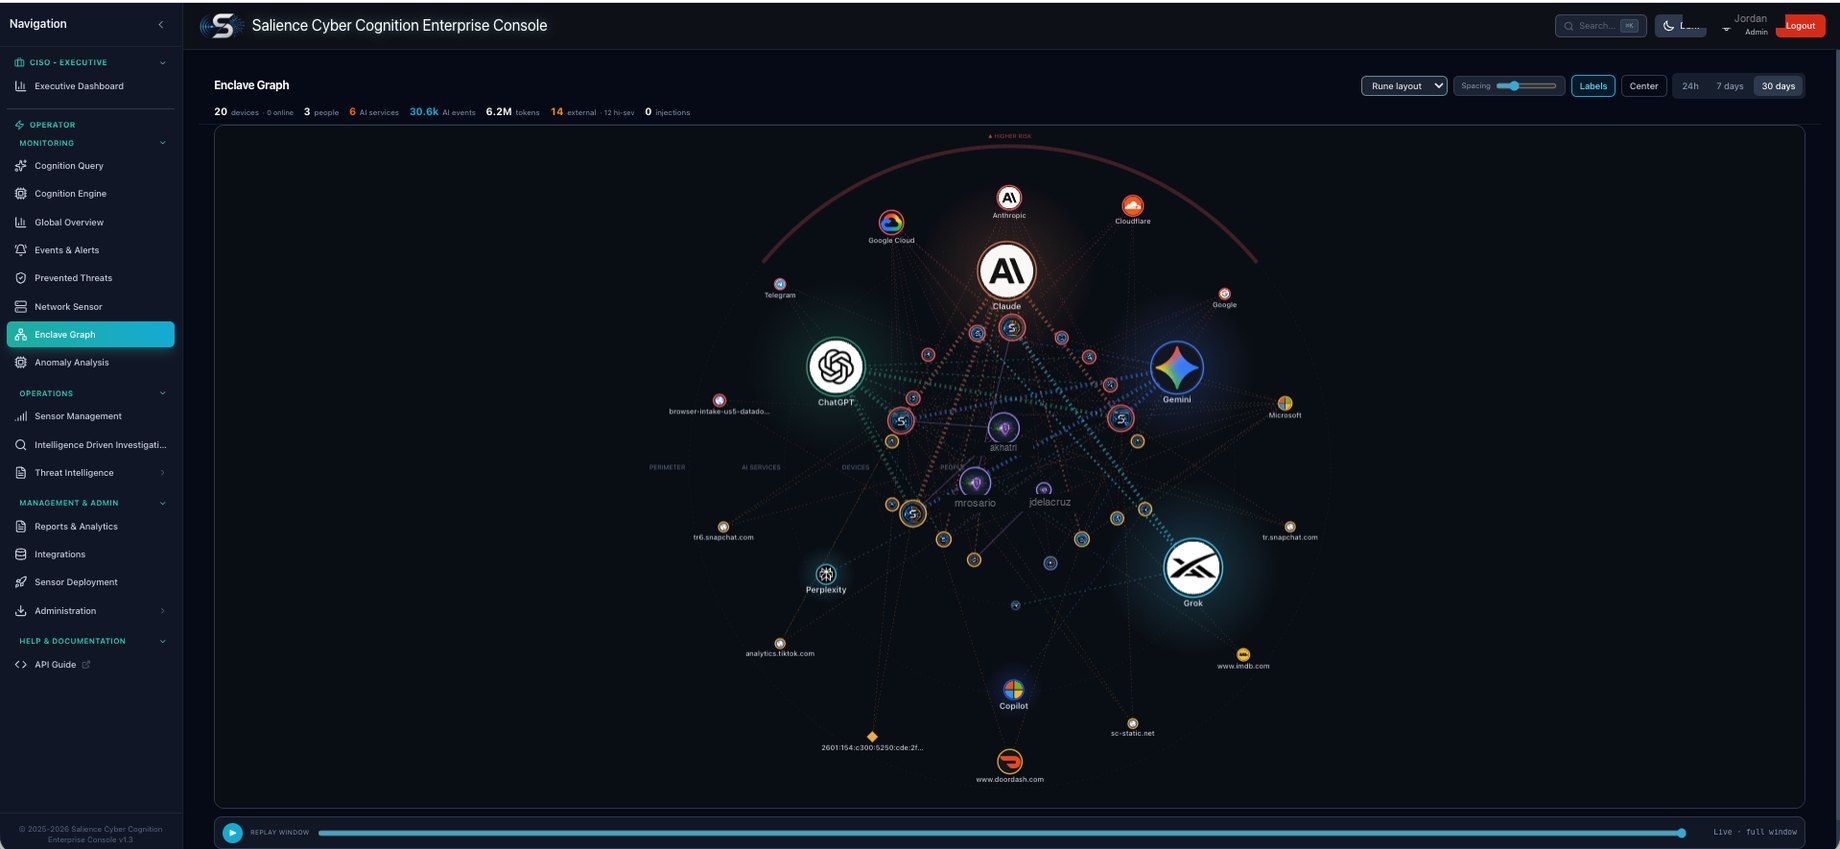
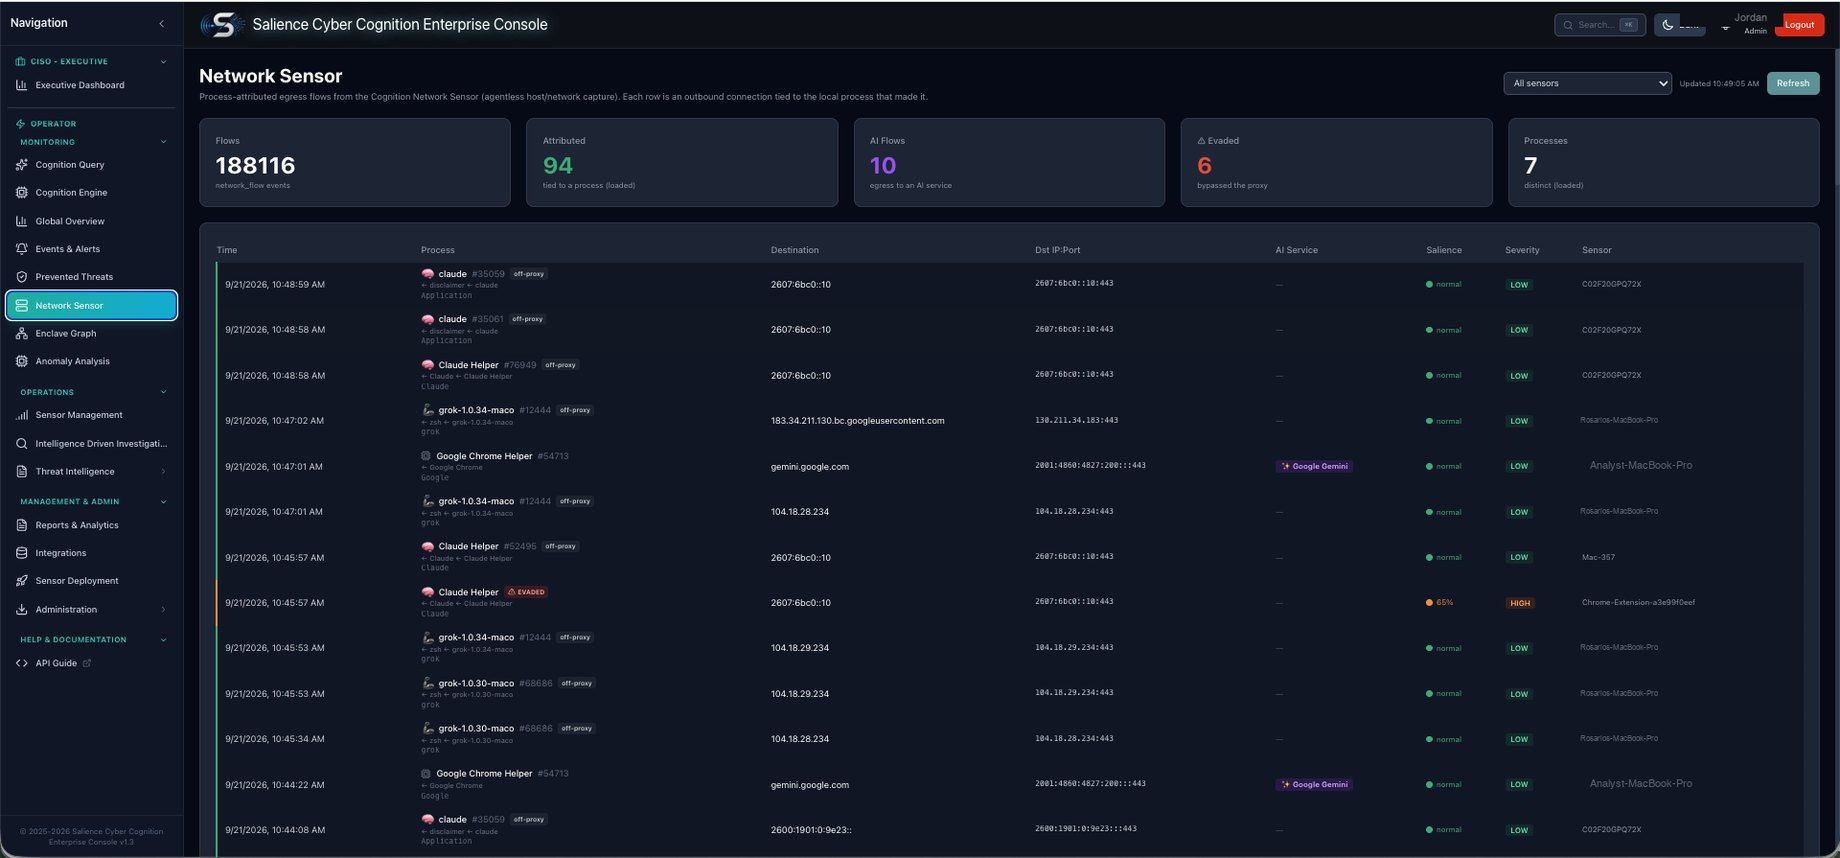
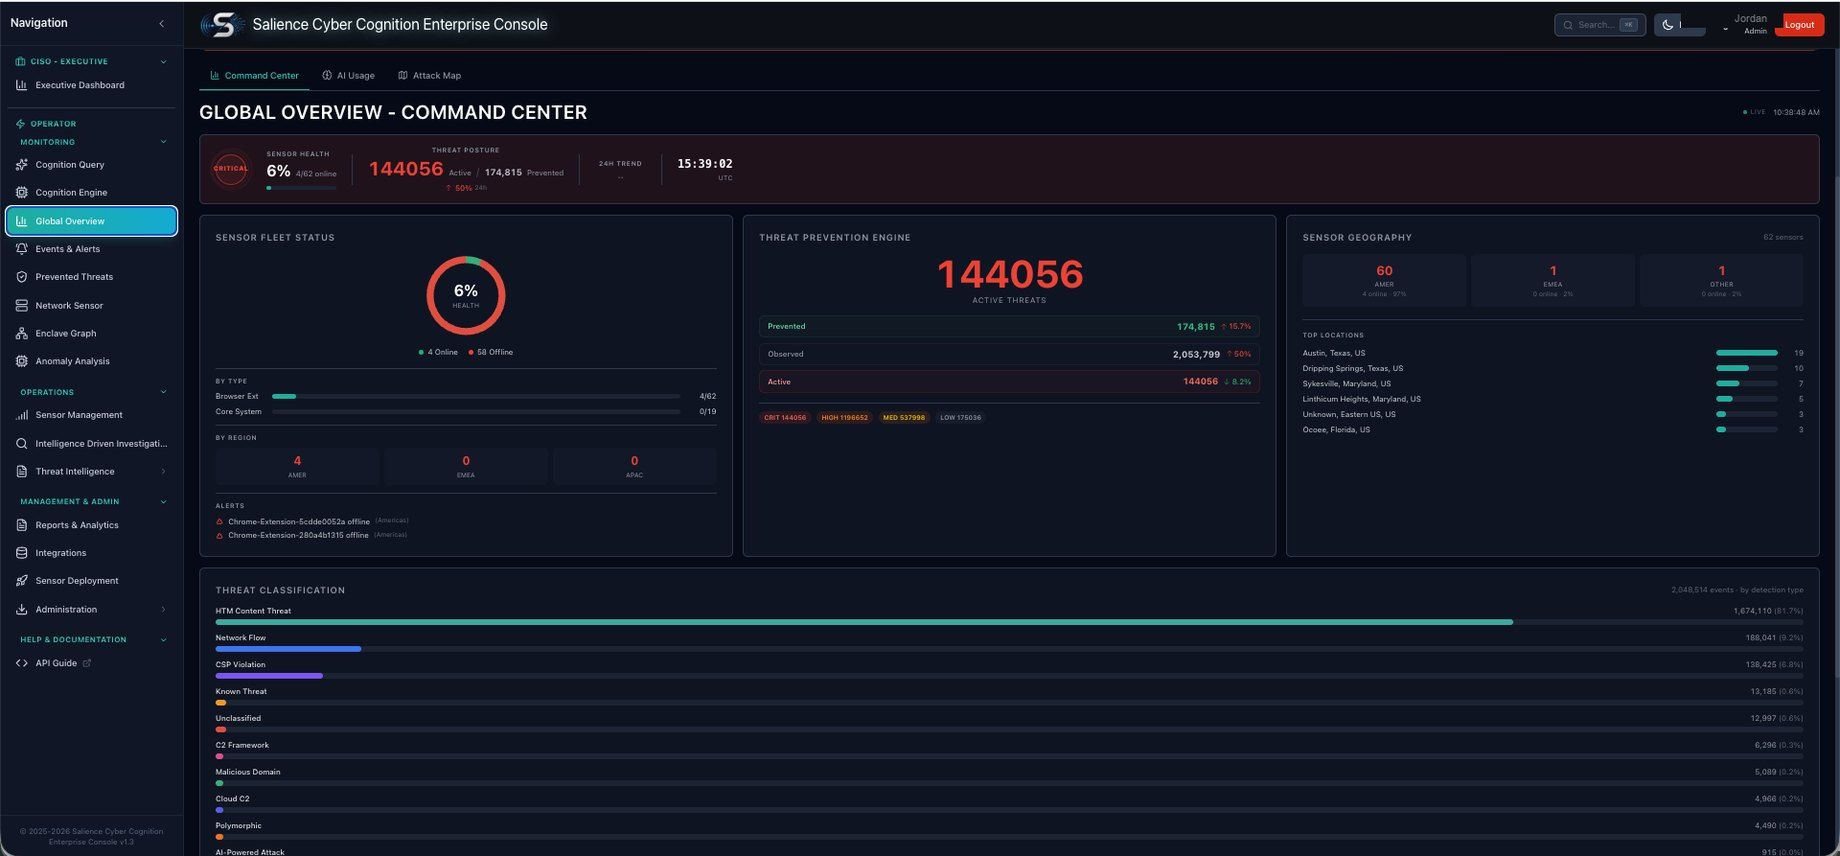
One platform, two data planes
Browser and operating system are one attack surface, not two. An interaction that starts in a GenAI session and ends in a running process is a single story — read as one here, rather than arriving as two alerts in two consoles for someone to reconcile afterwards.
| One decision loopCognitionAI Engine™ | ||
|---|---|---|
| Browser planeBrowser Sensor | System planeSystem Sensor | |
| Where it runs | In the browser session, in-page | In userspace, on native OS APIs |
| What it reads | Prompts · GenAI sessions · tool calls | Processes · agents · AI-created artifacts |
| Kernel surface | None — runs in-page, not on the operating system | None — no driver, kernel extension, EDR hook or Ring 0 |
| Platforms | Chrome · Chromium · Edge · Safari | Windows · macOS · Linux |
| Where it acts | At the point of interaction | At the point of execution |
On the operating-system plane, the System Sensor runs three engines — network, process and filesystem — correlated under a single user, process, and session identity:
Intercepts and decodes AI-related network traffic to reveal model interactions, prompts, responses, and data movement.
Associates every AI connection with its originating process, and identifies applications attempting to bypass approved AI channels.
Tracks what AI accesses and what it creates — maintaining lineage even when AI-generated files or binaries are executed later, outside the original session.
Together, the System Sensor and the Browser Sensor provide end-to-end visibility from user interaction to endpoint execution — one audit trail, with a named user and process behind every AI action, human or agentic, and no kernel-based monitoring to carry.
Explore the PlatformEveryone says “AI security.”
Almost nobody means this.
Put a language model in the decision path and you take on its exposure and its update cycle. Ship telemetry to a server and you take on the delay. We did neither — a model judging a model is a different tool for a different job.
| Salience Cyber | Model-judged AI security | Post-collection analytics | The stack you already own | Policy only | |
|---|---|---|---|---|---|
| Where it sits | In-line, at the point of interaction | In the request path, as a proxy or gateway | On a server, after the fact | On the host and in the log, after execution | Nowhere. It is a document |
| What it reads | Intent | A model's reading of the text | Logs | Artifacts and behaviour | Nothing |
| Can the decider itself be talked to? | No language in the decision path to address | It reads attacker-controlled text by design | Not in the path; it does not decide | Not in the path; it decides after execution | The policy cannot. The person can |
| Zero-signature attacks | Anticipated | Bounded by what the model recognises | After the fact, on a copy | Stops what it has seen before | Unaddressed |
| Decision path | Microseconds — no model round-trip, decided in-process | A model round-trip, per interaction | Minutes to hours | After execution | A person, if someone reports it |
| What it costs | Flat. No per-token metering | Metered per token or per call | Per GB stored and queried | Per endpoint, plus retention | Nothing to license. Everything to enforce |
| What it adds to your attack surface | Two userspace sensors. No kernel driver, and no model in the decision path | A model in the decision path, with that model's exposure and update cycle | A second copy of your data | A kernel driver or an agent | Nothing technical |
| What you are left with | The hostile interaction is neutralized before it executes | A verdict from a model, and an alert | A report | A ticket | An assumption that people complied |
Same words. Different architecture. Different outcome.
The alert is the incumbent's business model.
See the CognitionAI Engine neutralize an AI-forged attack before it runs.
Request a Demo